User-Friendliness & Flexibility
Why IDM-Portal?
The IAM Solution for Identity Governance & Administration
Whether in companies, public authorities, clinics or social institutions: Wherever people join, leave or change roles, access complexity arises. The FirstWare IDM-Portal brings Identity Governance & Administration into practice, supporting your IT and making it usable for your specialist departments.
Made in Germany
GDPR & NIS2-compliant
25 years of IAM expertise
Vendor & cloud-independent
What is the FirstWare IDM-Portal?
Flexible IAM solution for Identity Governance & Administration
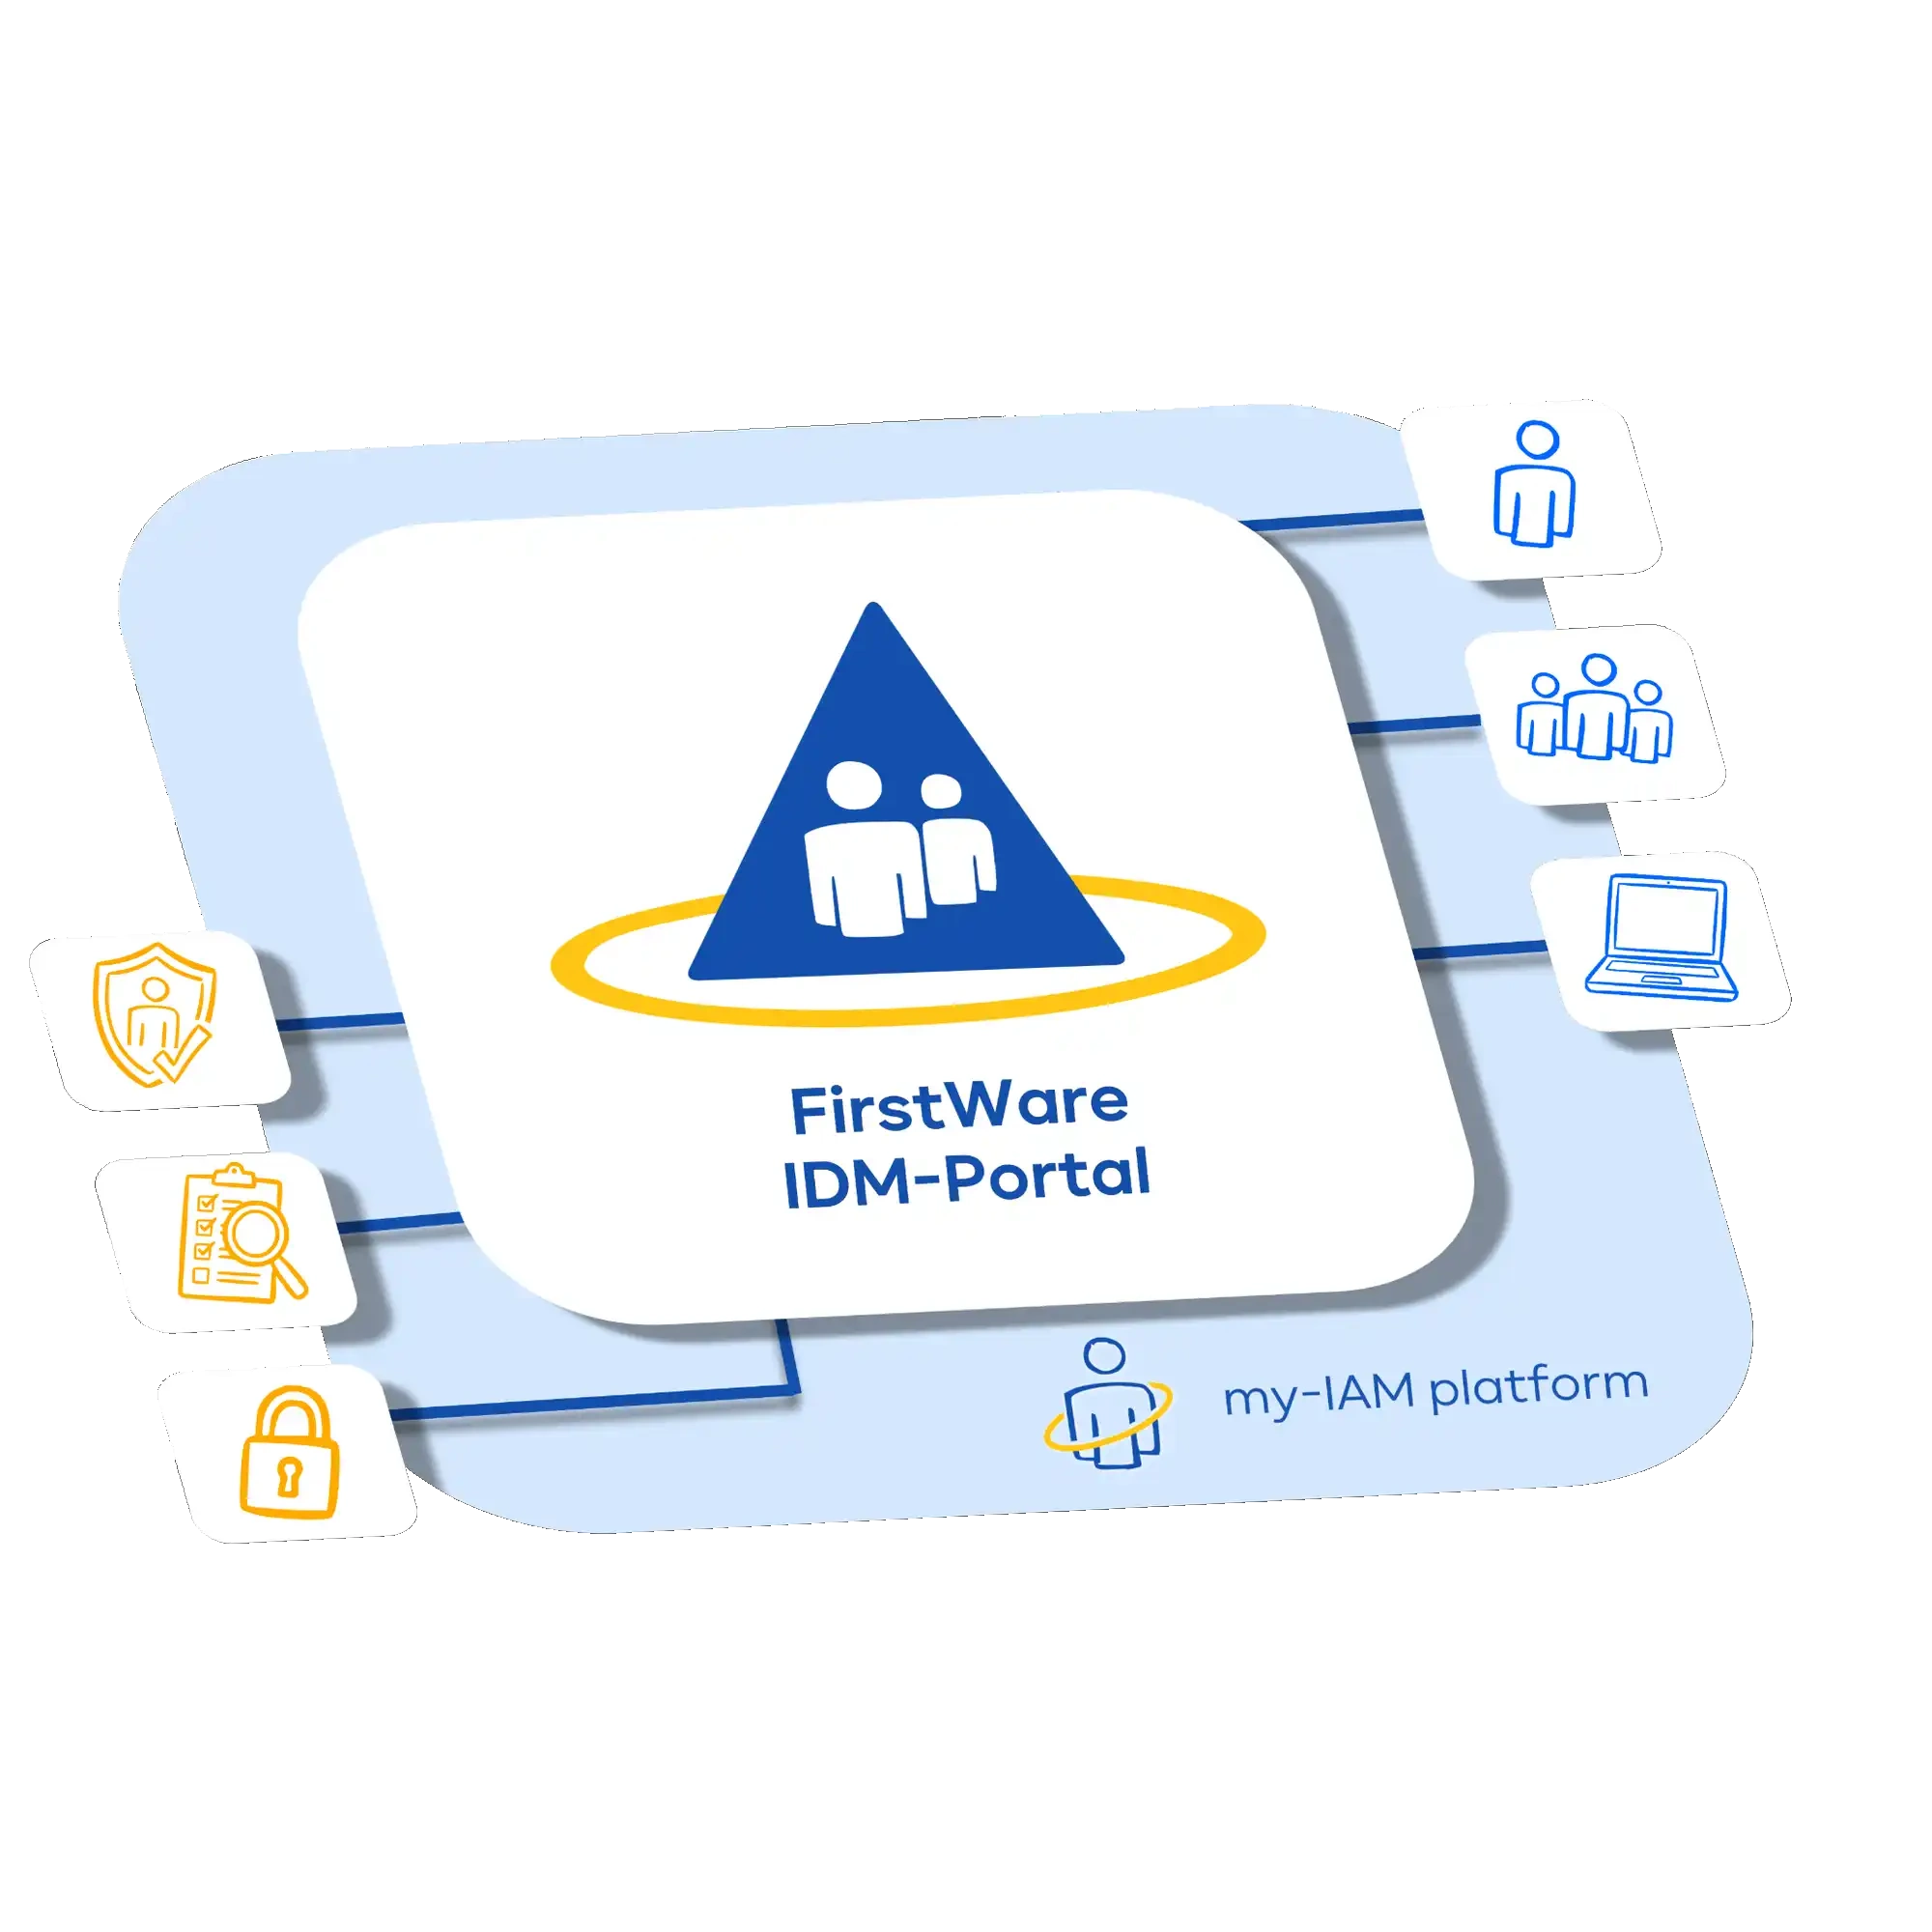
The FirstWare IDM-Portal is a user-friendly IAM solution for automated provisioning and lifecycle management of all identities and groups in complex, hybrid IT landscapes.
Through targeted delegation and role-based access management, it enables specialist departments to maintain identity data and permissions independently, complemented by powerful Identity Governance & Administration (IGA) features such as audit logs, recertifications and compliance reporting.
Powered by my-IAM
The FirstWare IDM-Portal is based on the my-IAM technology platform. As a powerful engine in the background, my-IAM enables seamless integration of any IT systems and cloud services. This combines an intuitive portal interface with the limitless connectivity of a modern integration platform.
Key Points
at a glance
This is what makes the FirstWare IDM-Portal stand out, from usability and security to fair licensing:
Self-explanatory, user-friendly interfaces
Clear visibility of all access rights
Low implementation and training costs
Flexibly adaptable to your requirements
All identity types: employees, customers, suppliers, NHI
Cloud, hybrid and on-premises capable
High savings potential, fast ROI
Fair, transparent licensing model
Sovereignly developed and supported in Germany
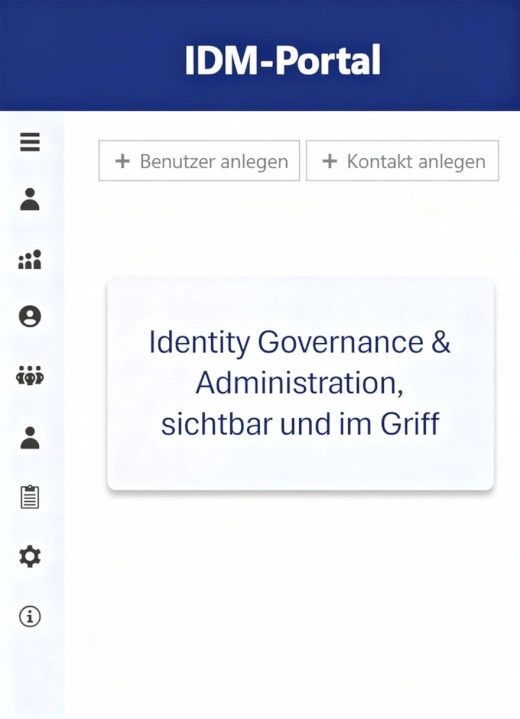
Designed for decision-makers. Loved by administrators.
The FirstWare IDM-Portal is designed for everyone involved with identities and access, from strategic decision-making to daily operations.
For CIOs, CISOs & IT managers
(strategy, ROI & governance)
- Noticeable cost and time savings: Save up to 80% of administrative effort in identity management and reduce unnecessary SaaS licensing costs.
- Reliable audits: Fully automated, audit-proof logging of all actions supports compliance with NIS2, GDPR, ISO 27001, TISAX and BSI IT-Grundschutz.
- Consistent zero-trust architecture: Identities only have the permissions they actually need at any given time.
- Future-proofing without vendor lock-in: An open IGA architecture that flexibly adapts to your multi-cloud strategy instead of tying you to a single ecosystem.
For IT admins & specialists
(operations & automation)
- One central interface: Manage all local and cloud-based directories from a single, user-friendly web interface without constantly switching between admin consoles.
- Significant relief from routine tasks: Intuitive delegation to specialist departments and self-service options reduce recurring helpdesk tickets by up to 60%.
- Full control via RBAC: Delegate tasks to your local IT teams or specialist departments while retaining full control over roles and permissions.
- High flexibility without development effort: Rename attributes, hide fields and configure rule-based automations without complex database extensions.
Your IDM-Portal,
made by people, for people
The first IGA system that needs no explanation
Decision-makers and administrators are not the only people who work with the IDM-Portal every day. Specialist departments, HR managers and employees also use it in their daily work.
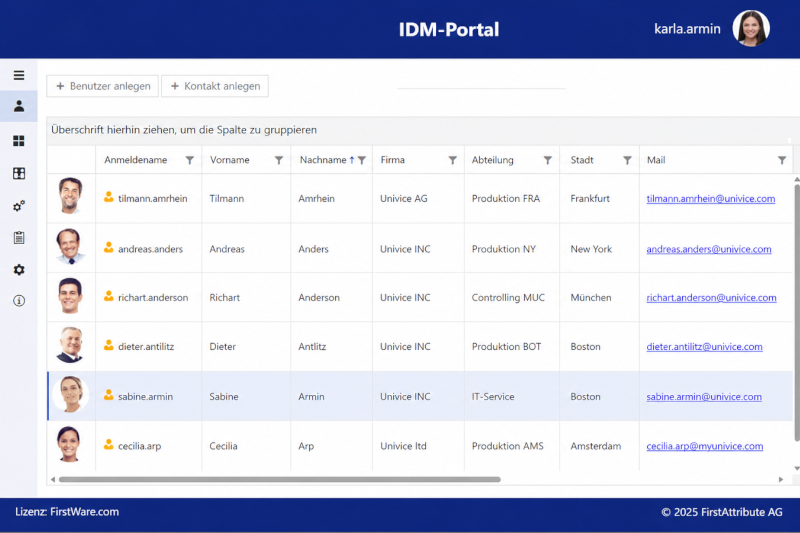
Human-centric design is our guiding principle. People who use the portal need to trust it, and it must enrich their working day instead of complicating it. That is why our interfaces are designed so that even non-technical users can maintain identity data and handle access approvals intuitively in their daily work. This makes complex permissions immediately understandable and helps prevent misconfigurations.
With the IDM-Portal, you can also see at any time who has access to what. We call this "maximum access visibility". For IT, everything becomes transparent; for users, it remains invisible in the background.
What Identity Governance & Administration
actually means
Identity and Access Management (IAM) is the operational foundation. It ensures that the right identity gets access to the right resources.
Identity Governance & Administration (IGA) is the area that manages, controls and documents these identities.
It rests on three pillars, each covering a specific part of this task:
Administration
The entire lifecycle of an identity is covered, from creation to deactivation.
Governance
Policies such as recertification and segregation of duties are actually enforced.
Reporting & Analytics
Every decision is documented in an audit-proof way and remains auditable at any time.
Everything your Identity Governance & Administration needs
All the following areas come together in a single interface: the FirstWare IDM-Portal.

Access Management
Access management, often the largest cost block in ongoing operations, becomes visible and manageable.

Identity Lifecycle Management
Every identity is recorded and automatically managed from entry to exit.

Identity Delegation
Specialist departments handle many administrative tasks themselves, giving your IT more time for higher-value work.

Role-Based Access Control (RBAC)
Reduced attack surface because no one has more permissions than their role requires.

Profile & Self Management
Fewer tickets for your IT because employees and teams manage data and access themselves.

Approval
workflows
Secure approvals by the right decision-maker, quickly and easily within daily operations.

IAM Automation
A single change is enough; everything else runs automatically, immediately or on a scheduled basis.

Resource
Management
All resources are recorded, making it clear at all times who is responsible for what.

System Integrations
One interface for your entire system landscape instead of one application per system.
The same problem across industries
As different as industries may be, their core problem is often the same: identities are created once, while access rights change constantly. This is exactly where the FirstWare IDM-Portal comes in.
Companies
Growth, new projects, departmental changes: the larger your organization, the faster the number of access rights that need to be managed grows.
Public authorities and agencies
Federal structures and multiple locations require clear, traceable responsibilities, not a single central IT team expected to handle everything alone.
Clinics
Rotating staff, shift work and highly sensitive patient data come together. Every access right must be traceable and immediately revocable.
Logistics providers
Many locations, high turnover, seasonal staff: access management has to work just as fast as day-to-day operations.
What sets the IDM-Portal apart from traditional IAM systems
Many IAM solutions focus on the identity itself: creating and deleting accounts. The real effort, however, comes afterwards in the ongoing maintenance of access rights.
The FirstWare IDM-Portal addresses exactly this point. It combines user-friendliness with real governance depth, remains vendor- and cloud-independent and integrates flexibly into hybrid system landscapes without tying you to a single provider.
What also sets the FirstWare IDM-Portal apart is the depth of its delegation. Responsibility can be delegated not only broadly, but down to individual attributes to specialist departments or decentralized IT teams, more granularly than most traditional IAM systems even provide for.
You also decide on the operating model yourself: fully cloud-based, hybrid or on-premises. As your needs grow, you can extend the configuration yourself instead of waiting for a development project. We adapt to your requirements, not the other way around.
Frequently Asked Questions
Frequently asked questions about the benefits, use cases and features of the FirstWare IDM-Portal for secure digital identities and efficient IAM.
What does the FirstWare IDM-Portal do in one sentence?
The FirstWare IDM-Portal is a solution for user and access rights management, specializing in Identity Governance & Administration (IGA), the management, control and traceability of digital identities.
How are IAM and IGA connected?
Identity and Access Management (IAM) is the operational foundation. It ensures that the right identity has access to the right resources. Identity Governance & Administration (IGA) is the area we specialize in; it handles the management, control and traceability of these identities.
Do I need additional IAM tools besides the IDM-Portal?
No. The FirstWare IDM-Portal covers Identity Lifecycle Management, Access Management, delegation, approval workflows and other core IGA functions in a single interface.
How quickly is the IDM-Portal ready for use?
Thanks to its high compatibility with existing infrastructure, implementation is significantly faster than in traditional IAM projects. The exact timeline depends on your individual system landscape, which we will be happy to discuss with you personally.
How much does implementation cost, and how quickly does it pay off?
This depends on the size and complexity of your organization. Many companies see savings in the first year, especially through reduced manual effort and avoided licensing costs.
Is a fair licensing model guaranteed, even as the number of users grows?
Yes. Our licensing model is transparent and designed around your actual growth, with no hidden costs or pressure to buy oversized packages. We are a fair and collaborative company and value strong, long-term relationships with our customers.
How much training effort is required for implementation?
Significantly less than with traditional IAM systems. The self-explanatory interface of the IDM-Portal is designed for specialist users without technical knowledge. Our goal is to make the portal so user-friendly that it is not only intuitive to use, but also enjoyable to work with. Extensive training for your employees is not required.
Let's Talk
We are here for you da
Would you like to know why the IDM-Portal fits your IAM requirements? Call us at +49 8196 998 4330 or use our contact form.