The FirstWare IDM Portal now also runs on STACKIT, Schwarz Group’s European cloud. Find out why distributed identities are key to greater independence, and how sovereignty begins with identity data.
Since August 7, 2026, FirstAttribute has had a second infrastructure provider alongside Microsoft: STACKIT, operated by Schwarz Digits Cloud GmbH & Co. KG. For us, this is more than a technical addition. It gives our customers the freedom to choose where their identity data is stored and who can access it.
Inhaltsverzeichnis
Sovereignty is a question of architecture
One question keeps coming up in strategy discussions: How can we become a little more independent without abandoning proven structures overnight? Rarely does this mean making a radical break. It is about finding a way forward, step by step and under control.
Our answer: Sovereignty means distributed identities.
 Consolidating identity and access management within a single infrastructure creates a single point of dependency. This is not necessarily a problem as long as conditions remain stable. But in an emergency, that dependency can be difficult to undo. Distributed identities, the ability to manage identities, roles, and permissions across multiple platforms and infrastructures, give you more freedom of choice. Workloads can run wherever they are best suited from a business, regulatory, and strategic perspective.
In technical terms, this means separating governance from the directory services and underlying infrastructure. The IGA layer becomes the central control point, regardless of which cloud hosts the IDM Portal or which identity providers are connected, for example, Microsoft Entra ID, Active Directory, Keycloak, or other directories and applications.
Get in touch. We’re happy to share our experience from projects in the public sector, healthcare, and with operators of critical infrastructure.
Why Identity Governance & Administration?
Identity Governance & Administration (IGA) is the backbone of access security. That makes identity data some of an organization’s most sensitive data. IGA helps keep track of identities and their associated permissions: Who has which rights, why were they granted, and when should they be revoked? To do this, IGA connects HR data, directory services, business applications, and cloud services.
The pressure is growing. NIS2 and the GDPR require demonstrable control. At the same time, the number of non-human identities is increasing, including service accounts, bots, and machine identities. Mid-sized businesses and critical infrastructure operators in particular can quickly find themselves stretched to their limits.
Where systems are hosted matters, too. Under the U.S. CLOUD Act, U.S. authorities may, under certain circumstances, access data held by U.S. providers, including data stored outside the United States. Every organization assesses the significance of this differently, but for many it is a factor in their risk assessment.
Microsoft remains an important partner for FirstAttribute. Azure continues to be a platform on which we host the FirstWare IDM Portal for many customers. But we believe that true freedom of choice only exists when there is an equivalent alternative.
STACKIT: the European alternative
With STACKIT, we have a partner offering just such an alternative. The Schwarz Group’s cloud platform operates its data centers in Germany and is subject to European law. Its infrastructure has been attested against the BSI’s C5 criteria. This is an important assurance for public-sector organizations and critical infrastructure operators.
The Schwarz Group is investing heavily in new data centers and uses the platform at scale itself. You can find out more about STACKIT on the provider’s website.
What we heard at the Cloud X Summit
On September 16 and 17, 2026, we attended the STACKIT Partner & Cloud X Summit as a partner. The conversations and insights we gained there brought three developments into particularly sharp focus:
First: Demand is coming from the sectors we know. During discussions about hospitals and public authorities, IT leaders shared how they run services on STACKIT. One remark stayed with us: “Transformation is a decision, not a project.”
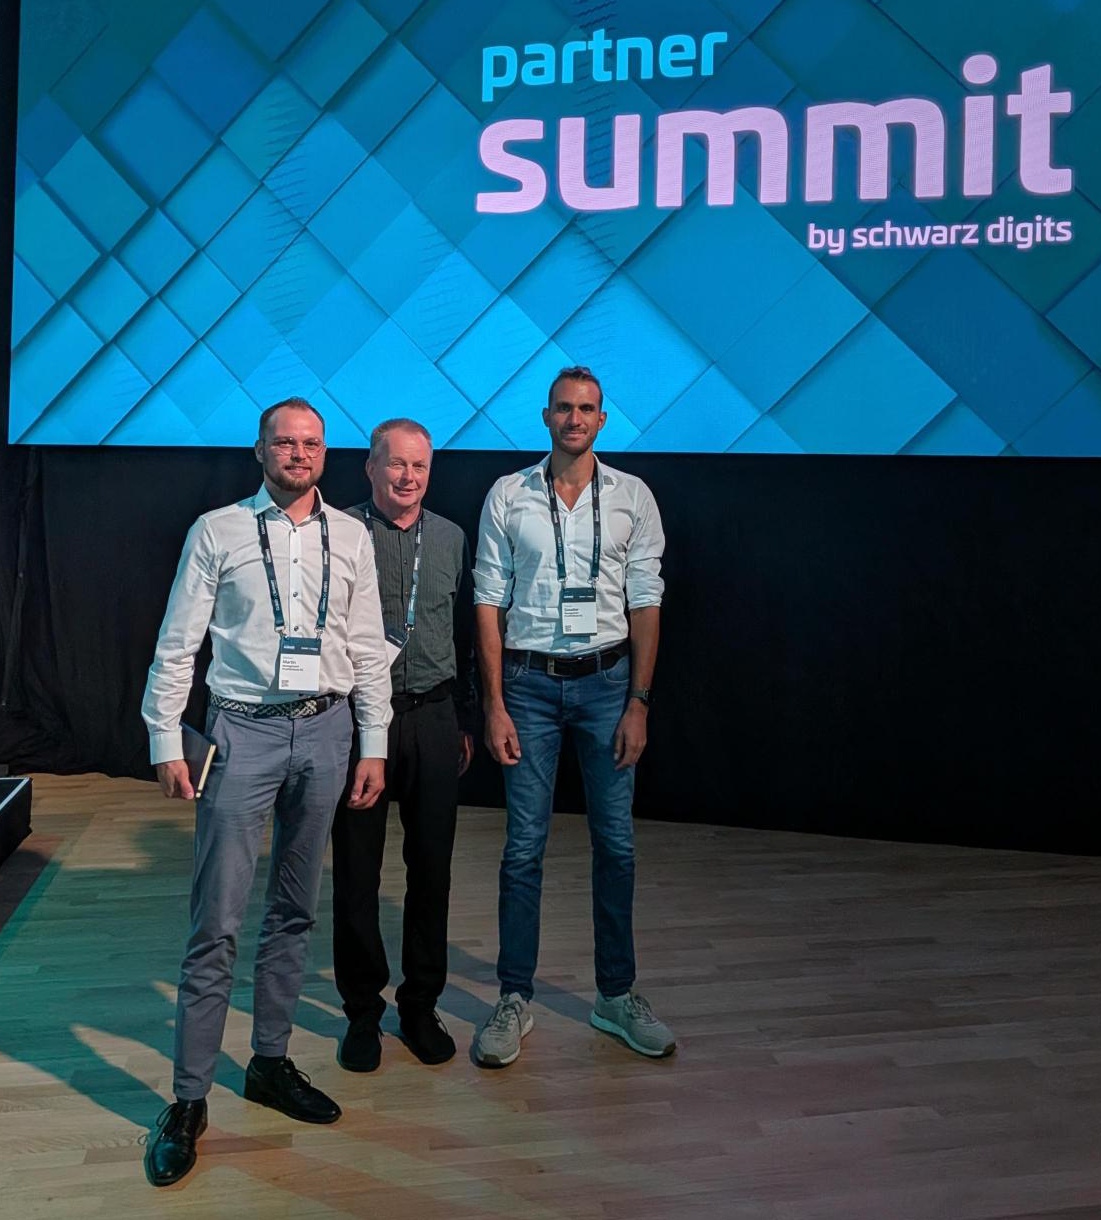
Second: The approach is pragmatic. STACKIT works with other providers, including SAP and Google Workspace. The guiding principle is that storage, encryption, and data sovereignty should remain under European control. We believe this is a sensible approach, especially for organizations that need to move forward step by step.
Third: The performance is impressive. One contact from the European software industry described STACKIT as one of the few providers able to deliver the resources needed to compete alongside the major international cloud providers.
The IDM Portal on STACKIT: what’s in the works
There is clear interest. We are speaking with customers in the public sector, healthcare, critical infrastructure, and financial services about initial target architectures. For many, the question is not whether they want to become more independent, but how. Separating governance from the infrastructure makes it possible to switch the underlying infrastructure step by step or run it in parallel. This takes the pressure off the decision. No one has to change everything at once.
The IDM Portal on STACKIT makes this journey possible, without requiring anyone to change everything at once.
Independence is a journey, not a leap
Digital sovereignty is not an either-or decision. Becoming more independent does not require a major upheaval. It requires an architecture that keeps your options open. Distributed identities make decisions reversible and dependencies manageable.
With Microsoft Azure and STACKIT, we will offer you two strong infrastructure options for the FirstWare IDM Portal. You decide where your identities are hosted, today, tomorrow, and in the future.
Get in touch. We’ll show you what a path toward greater sovereignty in identity management could look like. Plan your next step.