Precise access rights
Role-Based Access Control (RBAC)
Exactly the rights each role really needs
With Role-Based Access Control (RBAC) in the FirstWare IDM-Portal, you can automatically assign the appropriate permissions to each employee in your connected target systems based on attributes such as department, location, or job title. You define roles that automatically translate into specific permissions, across many connected systems.
Made in Germany
GDPR- & NIS2-compliant
25 years of IAM expertise
Vendor- & cloud-independent
Reality Check:
Why permissions get out of control without a role model
Without a clear role model, the number of access rights grows faster than anyone can keep track of.
Inconsistent assignment of rights
Two employees with identical positions have different access rights.
Overprivileged accounts
When in doubt, permissions are granted too generously.
Missing access slows down work
Essential permissions are missing, and work comes to a halt.
No answers during audits
In an audit, identifying who has access to what becomes a time-consuming investigation.
Role-Based Access Control with the IDM-Portal
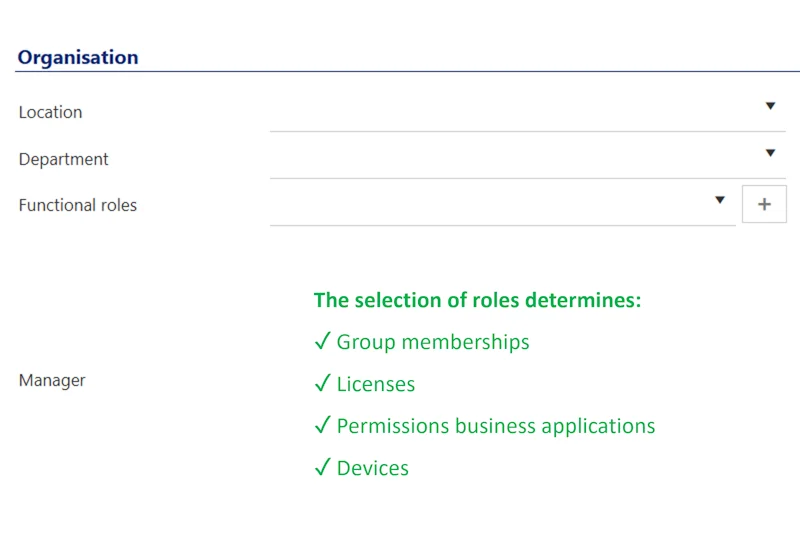
Tailored permissions in every target system
Roles that are automatically transferred
In the FirstWare IDM-Portal, you define roles based on attributes such as job function, department, or location. Each role is linked to the appropriate permissions in your connected target systems, such as AD group memberships, Entra ID roles, or access to line-of-business applications.
If an attribute changes - for example, due to a change in department or location - access is automatically adjusted. No one ever has more rights than their current role requires, across all connected systems.
Granular control down to the finest detail
Each role gets exactly the right combination
Standard roles cover the typical use cases, but not every employee with the same job function needs exactly the same permissions. Using additional, attribute-based rules (ABAC), you can selectively deviate from the standard for individual permissions without having to create a new role.
This allows you to grant individual members of a role temporary additional access - for example, for the duration of a project - while the rest of the role remains unchanged. Each exception is automatically revoked as soon as the specified time limit is reached.
Consistent permissions instead of case-by-case decisions
Same role, same access
Whether in Berlin or Munich, sales or production: Anyone in the same role receives the same permissions. This eliminates the need for individual agreements or special rules that accumulate unnoticed over time.
This also applies when new locations or departments are added. Instead of having to decide from scratch each time who is allowed to access what, you simply apply the existing role model to the new structure.
For your IT department, this means less coordination effort in day-to-day operations and a permissions structure that can be traced and explained at any time.
Faster decisions
Approvals that don’t have to go through IT
You can specify on a case-by-case basis who is authorized to approve a request - for example, the responsible manager or the owner of the affected resource. The IT department no longer needs to be involved.
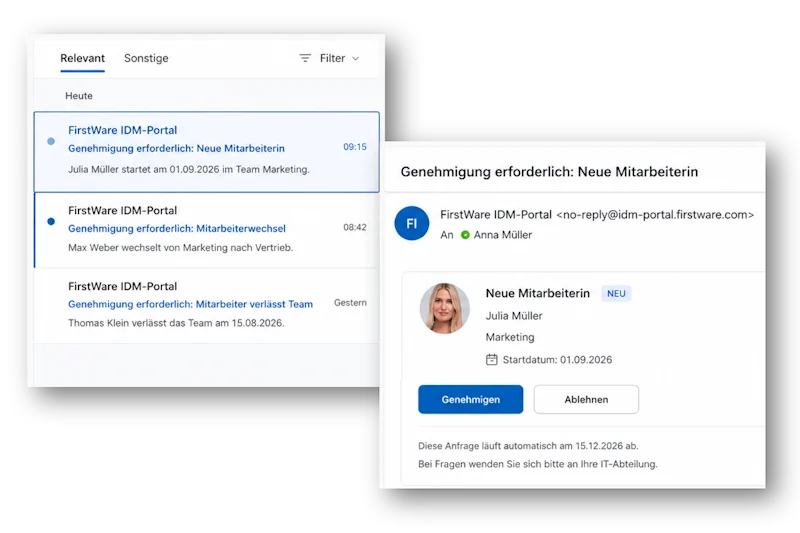
Whether a new employee joins the department or an existing employee requests access to a project folder: The person in charge is automatically notified by email and makes the decision right away.
As soon as a request is approved, the stored role model takes effect automatically: Permissions are set up automatically in exact accordance with the rules that apply to the respective role.
What is the FirstWare IDM-Portal?
Flexible IAM solution for Identity Governance & Administration
The FirstWare IDM-Portal is a user-friendly IAM solution for automated provisioning and lifecycle management of all identities and groups in complex, hybrid IT landscapes.
Powered by my-IAM – the underlying technology platform that enables seamless connection of any IT systems and cloud services.
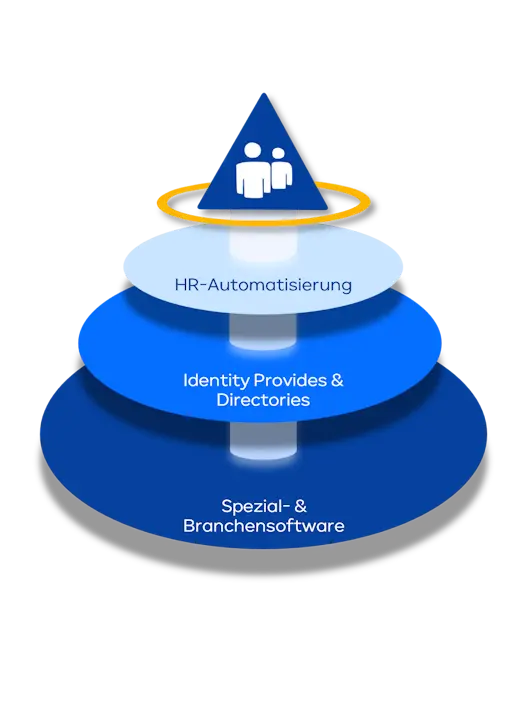
Role-based access control for your entire IT landscape
Whether cloud-native or hybrid: your roles and permissions apply consistently across all connected systems, including Microsoft Entra ID and other directory services.
HR integration
Personio, SAP SuccessFactors, SD Worx / Loga3
Identity Providers & Directories
Microsoft Entra ID, Keycloak, hybrid infrastructures
Specialized & industry software
Dedalus Orbis, SQL integrations, CSV- & API connectors
No matter how individually your system landscape has evolved, you get a single, consistent view of all identities, regardless of where the data originally comes from.
Your benefits

Automated assignment of permissions by role

Granular control by role and attribute

Rights follow the change in position

Consistent roles across all target systems

Approvals by departments

Audit- and compliance-ready
Frequently Asked Questions
Frequently asked questions about Role-Based Access Control (RBAC), central role models, targeted access control and secure rights assignment with the FirstWare IDM-Portal.
What is RBAC (Role-Based Access Control)?
RBAC (Role-Based Access Control) is a model in which access rights are assigned not to individual people, but to defined roles, for example based on function, department or location. Everyone with the same role automatically receives the same permissions.
How does automated role assignment with RBAC work in the IDM-Portal?
Based on attributes such as department, location, or job title, the IDM portal automatically assigns employees the appropriate role. These attributes can be sourced from a connected HR system, but can also be sourced from other source systems or maintained directly in the IDM portal.
The assigned role is linked to specific target system permissions, such as AD group memberships, Entra ID roles, or access to line-of-business applications. If an attribute changes - for example, due to a department transfer - the permissions are automatically updated.
What is the difference between RBAC and ABAC?
RBAC assigns permissions based on a fixed role, such as department or position. ABAC (Attribute-Based Access Control) goes one step further and also takes individual attributes such as location, project assignment or contract type into account to control access rights even more granularly and dynamically. The FirstWare IDM-Portal combines both approaches: roles provide the basic structure, while attributes refine it where needed.
What is the difference between RBAC and delegation?
RBAC automatically controls which permissions an employee receives in connected target systems, based on attributes such as department, location, or job title.
Delegation, on the other hand, determines who in the IDM-Portal is authorized to perform administrative tasks on behalf of others, such as creating new identities or resetting passwords.
Both mechanisms can be combined: A delegated role in the portal can itself use RBAC rules to automatically assign permissions in target systems.
Does RBAC also support segregation of duties (SoD)?
A clear role model is a prerequisite for effective SoD controls. Since each permission is assigned to a role, it is easy to track which combinations of roles or permissions a person holds during recertification processes. This allows critical combinations to be specifically identified and resolved at the organizational level.
Is implementing RBAC complex?
The initial role planning requires some preparation, but it is manageable. Our team supports you with best-practice experience from numerous projects so that your role model fits your organization from the start.
How granularly can permissions be controlled with RBAC?
Very granularly. You define not only whether a role has access, but also whether it may create, write and/or delete (among many other options), down to individual attributes and resources. Role-dependent views within the portal itself can also be controlled this way.
How does RBAC support compliance requirements?
A clear role model shows at all times, in a traceable way, who has access to what and why. This makes it much easier to comply with requirements such as GDPR, ISO 27001 or NIS-2, because permission structures can be easily demonstrated to auditors.
Let's Talk
We are here for you
Would you like to manage Role-Based Access Control securely with the FirstWare IDM-Portal?
Call us at 0 8196 - 998 4330 or use our contact form.