Faster processes
Identity Delegation
Responsibility where the knowledge is
With FirstWare IDM-Portal, you transfer responsibility for identities and access rights exactly where it belongs. Your departments handle Identity and Access Management without even noticing it. For them, it simply feels like a normal part of their workflow.
Made in Germany
DSGVO- & NIS2-konform
25 Jahre IAM Experts
Hersteller- & Cloud-unabhängig
Reality Check:
Why centralized IT management reaches its limits
Every small change ends up in the same place: your IT department. Yet the knowledge of who really needs what has long been somewhere else: in the departments, with team leads and at local sites.
IT as a bottleneck
Every change goes through the same central point.
Local IT with excessive permissions
Local IT teams are often given global admin rights.
Departments wait for decisions they could make themselves
Team leads make the decisions but cannot implement them themselves.
Audit effort without traceability
Finding out who delegated what becomes a time-consuming search.
Your IAM Delegation with IDM-Portal
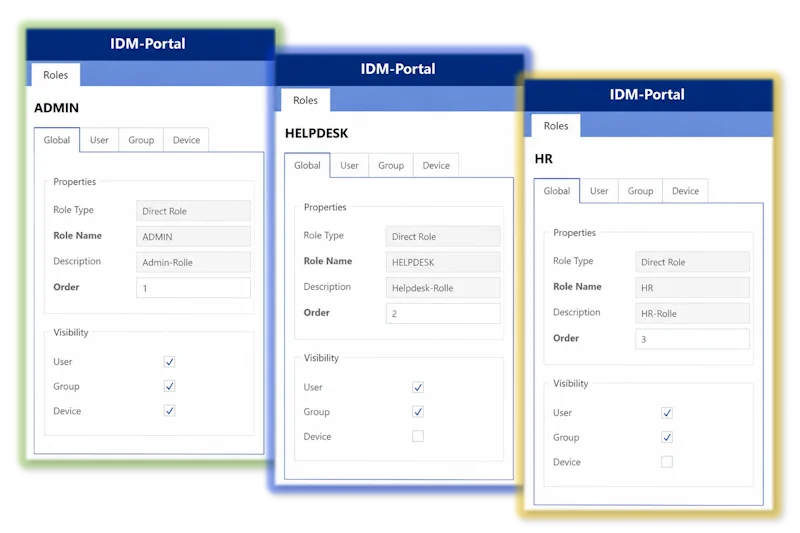
Role-based delegation to departments
Responsibility where the expertise is
Securely transfer the management of identities and access rights to the people who work closest to the data: your HR department, team leads or the owners of individual business applications.
FirstWare IDM-Portal handles the technical implementation in the background, while your key users complete exactly the tasks relevant to their area through tailored delegation roles.
You can specify, down to the attribute level, who is allowed to view and edit what. You have just as much flexibility in determining how these roles are technically defined.
Task sharing with decentralized IT teams
Within IT, too: only as much access as necessary
IAM delegation works just as well within your own IT organization. Especially in companies with multiple locations, local IT teams often work with far broader permissions than they actually need.
With IDM-Portal, you limit your local IT team's permissions precisely to their own area of responsibility. An administrator in Munich manages only identities in Munich, not the entire company.
The same applies independently of locations: if, for example, eleven administrators currently have direct access to AD or Entra ID, that group can be significantly reduced. Only a few retain full directory access, while everyone else works securely through the portal.
Intuitive, self-explanatory operation
Zero training for your departments
With our solution, you move IAM tasks directly to the responsible people in the business department.
Anyone who uses a smartphone on a daily basis already possesses all the skills required to use our IDM-Portal interface: managers and staff can manage access rights effortlessly and without error as part of their day-to-day work, without the need for training and without perceiving it as an IT task.
This immediately takes the pressure off your IT department. At the same time, every delegated decision is documented in a traceable manner, which is a clear advantage during audits and internal reviews.
Reliable traceability as part of your IGA
Delegation that remains audit-ready at all times
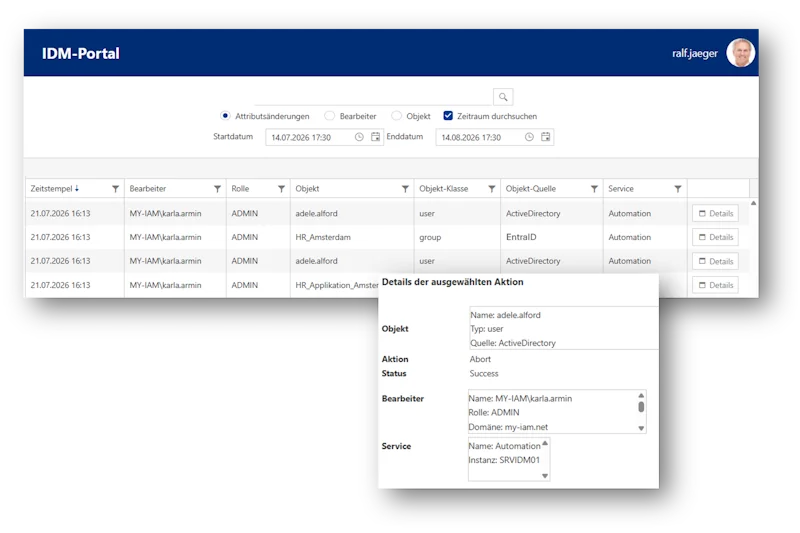
Handing over responsibility does not mean losing control. Every delegated action, whether performed by a business department or local IT, is logged in an audit-proof manner: who received, changed or revoked which permission and when? This useful history supports you in every audit.
Through a dedicated audit role, you grant auditors and security officers read-only access to this history without allowing them to make changes themselves.
Insightful data for better decisions
IAM Delegation that can be analyzed
Traditional log files are often technical and difficult to read. Cryptic codes and system names make any meaningful analysis difficult; often, they cannot even be searched in a targeted manner.
The FirstWare IDM-Portal, on the other hand, logs delegation decisions in a clear, searchable and comprehensible format. Who delegated, how often was a permission used, and where are requests concentrated? This allows you to actually make use of this data, rather than being faced with unreadable log files that nobody would voluntarily search through.
What is FirstWare IDM-Portal?
Flexible IAM solution for Identity Governance & Administration
FirstWare IDM-Portal is a user-friendly IAM solution for automated provisioning and lifecycle management of all identities and groups in complex, hybrid IT landscapes.
Powered by my-IAM – the technology platform in the background that enables seamless integration of any IT systems and cloud services.
IAM Delegation, independent of your system landscape
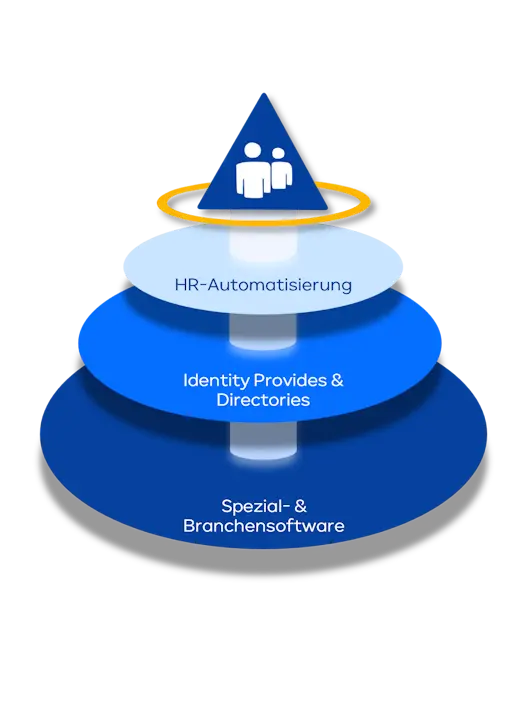
Whether cloud-native or hybrid, IAM delegation works regardless of where your identities are managed, including Microsoft Entra ID, Microsoft 365 and other connected directory services.
HR integration
Personio, SAP SuccessFactors, SD Worx / Loga3
Identity providers & directories
Microsoft Entra ID, Keycloak, hybrid infrastructures
Specialized & industry-specific software
Dedalus Orbis, SQL integrations, CSV- & API connectors
No matter how individually your system landscape has evolved, you get a single, consistent view of all identities, regardless of where the data originally comes from.
Your benefits

Noticeable relief for IT

Granular control down to attribute level

Zero training for departments

Scalable delegation for decentralized teams

Better local data quality

Traceable responsibility
Frequently Asked Questions
Frequently asked questions about IAM delegation, the secure transfer of responsibilities and decentralized identity management with FirstWare IDM-Portal.
What is IAM Delegation?
IAM delegation (also Identity Delegation) means the targeted transfer of responsibility for identities and access rights to people outside central IT. These can be departments, team leads or decentralized IT teams at individual locations.
Instead of processing every change centrally, responsible people decide for themselves within clearly defined roles and permission boundaries.
What is a role in the IDM-Portal?
A role in the FirstWare IDM-Portal defines who or what the “role holder” is authorized to manage. Specifically, this means which users or which specific attributes of those users the role holder is authorized to manage (read, edit, or delete).
Roles can be set up in various ways:
- by function (such as administrator, service desk, key user, or regular employee),
- by department (such as accounting, sales, or development), or
- by location (such as Dresden or Munich).
Every user must be assigned a role in order to make any changes in the portal at all.
What is the difference between IAM delegation and role-based access control (RBAC)?
Delegation determines who is authorized to perform administrative tasks on behalf of others in the IDM-Portal, such as creating new identities, modifying attributes, or resetting passwords. In other words, it concerns administrative rights within the portal.
RBAC (Role-Based Access Control), on the other hand, involves the automated assignment of permissions in the connected target systems, controlled by attributes such as an employee’s department, location, or job title.
The two mechanisms complement each other: A delegated role in the portal can itself use RBAC logic to automatically assign target system permissions instead of setting them manually.
Can I delegate within my own IT department, not only to business departments?
Yes. Especially across multiple locations, delegation can be tailored precisely to each area of responsibility. Your local IT team or local key users then manage only the identities at their own location instead of having global admin rights for the entire company.
Do I lose control as IT when I delegate tasks?
No. You define in advance exactly what each delegation role covers, down to the attribute level. Every delegated action is also logged in an audit-proof manner, so you can trace at any time who assumed which responsibility.
How granularly can delegation be controlled in FirstWare IDM-Portal?
Highly granular: You not only define which attributes a role is allowed to edit, but also which menus, functions, and self-service actions are visible to that role. For example, a site administrator sees only the workforce at their site, including an interface tailored precisely to their tasks.
How does Identity Delegation support compliance requirements?
Every delegated permission is documented without gaps. Through a dedicated audit role, auditors and security officers receive read-only access to this history without being able to make changes themselves. This is ideal for evidence in the context of ISO 27001, NIS 2 and TISAX.
How can I ensure that delegated roles don't “proliferate” over time?
Delegated roles should be reviewed regularly, just like traditional access rights. In the FirstWare IDM-Portal, you can view all delegated roles and their scope of permissions at any time and review them as part of recertification processes.
This ensures that a role still meets actual needs and does not accumulate unnecessary permissions over time - for example, due to substitution arrangements or project assignments that were never revoked.
How quickly does delegation pay off for my company?
Because delegation directly frees up resources in your central IT team, the effect often becomes visible within just a few weeks. We can determine together in a personal consultation how quickly it will pay off in your specific situation.
Let's Talk
We are here for you
Would you like to securely delegate identity and access management tasks?
Call us at +49 8196 998 4330 or use our contact form.